ESP Connected via WireGuard seemingly not working

Hi,

I’m using a known good WireGuard server (hosted in a Proxmox container) and can’t get my ESP32-C3 Super Mini to connect over it.

My home network (and the network it is connecting too) is setup as: 192.168.0.x
WireGuard is set up as: 10.0.0.x

In case it is not obvious, I have no idea what I’m doing at this point, so sorry if I have forgotten to add vital troubleshooting info!

Here’s my code:

esphome:
  name: dex
  friendly_name: Dex

esp32:
  variant: esp32c3
  framework:
    type: esp-idf

logger:

api:
  encryption:
    key: [REDACTED]

ota:
  - platform: esphome

wifi:
  ssid: !secret wifi_ssid_2
  password: !secret wifi_password_2
  use_address: 10.0.0.3    # The same IP as WireGuard has assigned the DEVICE

time:
  - platform: sntp
    id: sntp_time
    timezone: Europe/London
    servers:
     - 0.pool.ntp.org
     - 1.pool.ntp.org
     - 2.pool.ntp.org

wireguard:
  id: wg0
  netmask: 255.255.255.0
  
  # WireGuard address assigned to this DEVICE
  address: 10.0.0.3

  # Private key belonging to this DEVICE
  private_key: !secret wireguard_private_key

  # Public hostname/IP of your WireGuard server
  peer_endpoint: [REDACTED].duckdns.org

  # WireGuard server public key
  peer_public_key: !secret wireguard_server_public_key

  # WireGuard server port
  peer_port: 51820

  # Networks reachable through the VPN
  # peer_allowed_ips:
  #   - 0.0.0.0/0
  #   - 192.168.0.0/24

  peer_persistent_keepalive: 21s

  # Check periodically
  update_interval: 10s

What do you hope to gain with WireGuard?

esphome is hard enough to get working (until you do know what you are doing) with normal networking, doing it with a complicated network is just asking for problems.

You do need to get the logs from the device’s perspective. It probably has a clue as to what is configured incorrectly.

There are a lot of concepts one needs to understand to troubleshoot complex problems. Unfortunately, most tutorials assume things just work and don’t cover troubleshooting when they don’t.

Your device appears to be having a failure to communicate. It is likely saying why in its log.

I am trying to get sensor data from homeassistant to a display on the esp, with the esp being at my place of work.

I got this from the logs via a cable:

[20:34:12][D][wireguard:105]: Remote peer is offline (latest handshake timestamp not available)
[20:34:12][D][wireguard:229]: Starting connection
[20:34:12][I][wireguard:236]: Connection started
[20:34:12][D][wireguard:245]: Configuring allowed IPs list
[20:34:12][D][wireguard:252]: Allowed IPs list configured correctly
[20:34:22][D][wireguard:105]: Remote peer is offline (latest handshake timestamp not available)

Edit:
displaying of said data on the display works locally on another esp, so I have omitted it from my yaml that I posted to reduce complexity.

Hi, welcome to the forum.
Is it allowed at work to connect to a VPN (from WiFi)?

Yes, we all use some sort of VPN to remote into our home networks on a daily basis.

Also, is it possible to connect from a client on the server side to another remote client???

yes, that all works fully, including being able to see ESPhome’s port of 6053

You could replicate the WG client settings onto another system to see if that works (if you haven’t done so yet).

I have indeed done that, albeit just now ahaha. That works just fine via the Android app.

HA might have a problem with that?

From my experience in setting up home Wireguard the home network the vpn and clients have to be all on different networks.

I played with getting wireguard to connect a client esp32 on different network to connect back to ha but got nowhere.
The problem I think came down to VPN was on a device behind the router and I couldn’t work out how to route from router to VPN. It needed something mre than just port forwarding.

I cant see any peer allowed ips in your yaml

10.0.0.3 is mising the subnet. Its likely 10.0.0.3/32 (cidr rules)

EDIT: Somewhat fixed, please see below comment!

As it turns out, I did get it to connect… but I stupidly forgot to save the config, so I have literally no idea how I got here ffs…

If anyone can speculate on what my setting may have been as I have spent the last two hours trying every combination I remember…
Or if anyone knows how to reverse engineer the .bin file as I still have a copy of that!

Device log:

[18:53:48][C][wireguard:137]: WireGuard:
[18:53:48][C][wireguard:137]:   Address: 10.0.0.3
[18:53:48][C][wireguard:137]:   Netmask: 0.0.0.0
[18:53:48][C][wireguard:137]:   Private Key: [REDACTED]
[18:53:48][C][wireguard:137]:   Peer Endpoint: [REDACTED].duckdns.org
[18:53:48][C][wireguard:137]:   Peer Port: 51820
[18:53:48][C][wireguard:137]:   Peer Public Key: [REDACTED]
[18:53:48][C][wireguard:137]:   Peer Pre-shared Key: NOT IN USE
[18:53:48][C][wireguard:151]:   Peer Allowed IPs:
[18:53:48][C][wireguard:153]:     - 0.0.0.0/0.0.0.0
[18:53:48][C][wireguard:155]:   Peer Persistent Keepalive: 21s
[18:53:48][C][wireguard:157]:   Reboot Timeout: 900s
[18:53:48][C][wireguard:160]:   Require Connection to Proceed: YES
[18:53:48][C][wireguard:340]:   Update Interval: 10.000s
[18:53:48][C][esphome.ota:113]: Over-The-Air updates:
[18:53:48][C][esphome.ota:113]:   Address: 10.0.0.3:3232
[18:53:48][C][esphome.ota:113]:   Version: 2
[18:53:48][C][esphome.ota:113]:   Encryption: offered, plaintext accepted
[18:53:48][C][safe_mode:058]: Safe Mode:
[18:53:48][C][safe_mode:058]:   Successful after: 60s
[18:53:48][C][safe_mode:058]:   Invoke after: 10 attempts
[18:53:48][C][safe_mode:058]:   Duration: 300s
[18:53:48][C][safe_mode:079]:   Bootloader rollback: support unknown
[18:53:48][C][web_server.ota:256]: Web Server OTA
[18:53:48][C][api:271]: Server:
[18:53:48][C][api:271]:   Address: 10.0.0.3:6053
[18:53:48][C][api:271]:   Listen backlog: 4
[18:53:48][C][api:271]:   Max connections: 5
[18:53:48][C][api:278]:   Noise encryption: YES

I FIGURED IT OUT (kinda):

There is two public keys? one for the server and one for the device… I was putting the device public key into the .yaml when I should have been putting the server public key in.

Now the ESP connects to wireguard, but HA cant see it… But this feels like a firewall issue somewhere, unless anyone has any Ideas?

Have you added the device manually to ESPHome, not the builder but the integration using its IP address? It isn’t going to see it automatically like it normally does.

Settings > Devices & Services > ESPHome

Then click the add device button and enter it’s IP address 10.0.0.3

I have tried, but it cannot find the ESP.
What makes me think its a firewall issue is the box was pre-populated with the 10.0.0.3 IP address, so ESPhome knows my ESP is out there!
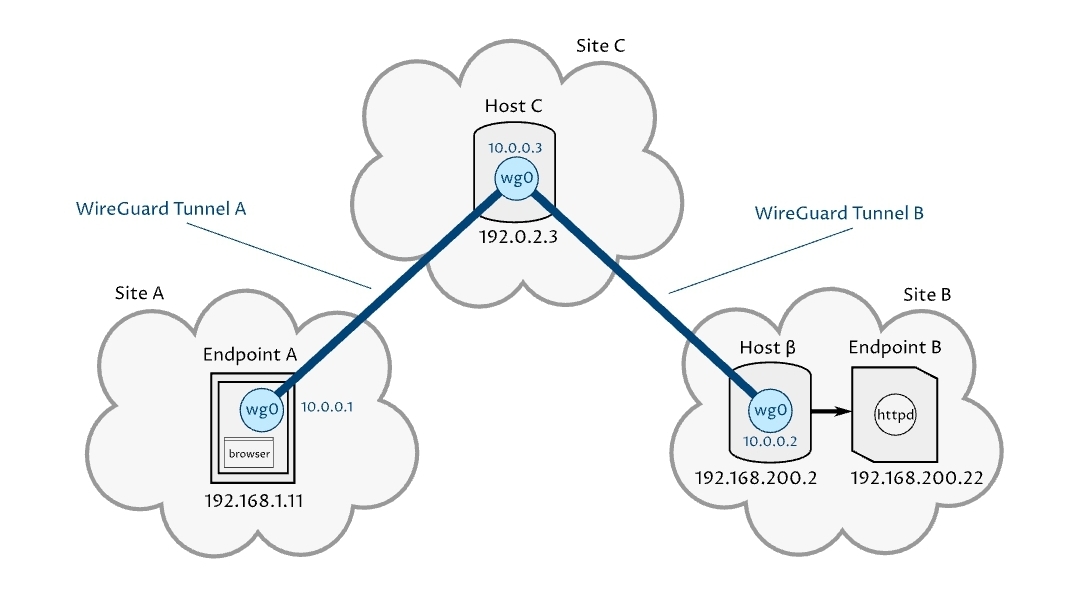
You wont find it using mDNS as its on a different network I feel.

From what I understand, it is on a different network as its on the WireGuard network (10.0.0.X) and my home network is 192.168.0.X

If you install the WireGuard client on your phone can you access HA’s web front end using it’s 192.168.0.x address through the VPN?

Yes, I can reach HA via the VPN.

Edit: I can see my whole network through my phone (I do plan on locking down the ESP once it’s all working)

Using that tunnel can use use an ip scanner and see your phones ip address on the same network HA is on?