Hey folks, I've built a MCP server for ESPHome to allow you to interact with it directly from whatever AI you're using (in my case, Open Design + Claude Code to make pretty UIs).
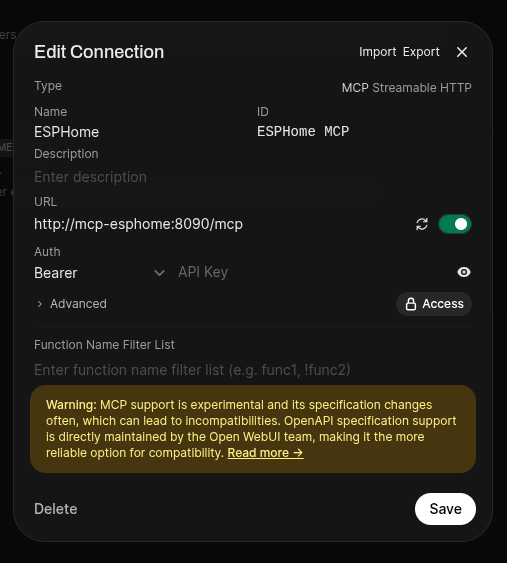
I have the docker running on Portainer and connected to ESPHome. But connecting it to Open WebUI hasn't worked yet. Seems to me that the issue is that the docker image doesn't support OpenAI connection types?
How is this different from the MCP server for Home Assistant if ESPHome is an integration on Home Assistant? Wouldn’t Claude be able to see ESPHome through the integration?
In other words, if I have Claude on the Home Assistant MCP server, what would this integration bring to the party.
Note- I have not ventured into MCP for Home Assistant yet, so this is all speculation.
Same differentiation as running Claude code on a HA server’s config folder V. Connecting to that servers MCP tools.
When you need to have an agent edit files on the server you use a direct file repo. Give you tons of power. Can do lots of stuff (and break lots) by having direct access to the filesystem. BUT.
When you want to reboot it? Use that systems predesigned toolset for maybe consistency checks or possibly observe your own code in native env? Do I write a file to make the system reboot? Nope.
THAT is a tool call. Using MCP (in this case.)
Look at the tools provided in this kit. - they allow the agent to see the state of an esphome device from. The admin side. Restart it, get it’s logs etc.
So you could use this inside your HA agent if you want to let it manage esphome (personally never.) you could use it as an mcp tool surface for codex or Claude or opencode or whatev… And they could do the same whether or not you allow the agent to access the filesystem os up to you.
Pair that with a competent code agent that you trust and can write esphome yaml and it can both write the code and deploy it, read it and edit it in a cyclic automated improvement loop…
For me this would exist as a tool for Nyx (my live test agent who does have filesystem access to my test dev ha box.
Where running this MCP server is handy, is that I don’t have to use Claude with it and expose all of my HA stuff to a cloud LLM.
I try to self-host as much as possible, especially when sensitive information is concerned.
For all my configs there’s a HARD wall between config and Frontline action. This falls on the sys config side. That’s all. Personal choice. But that’s where it comes from.