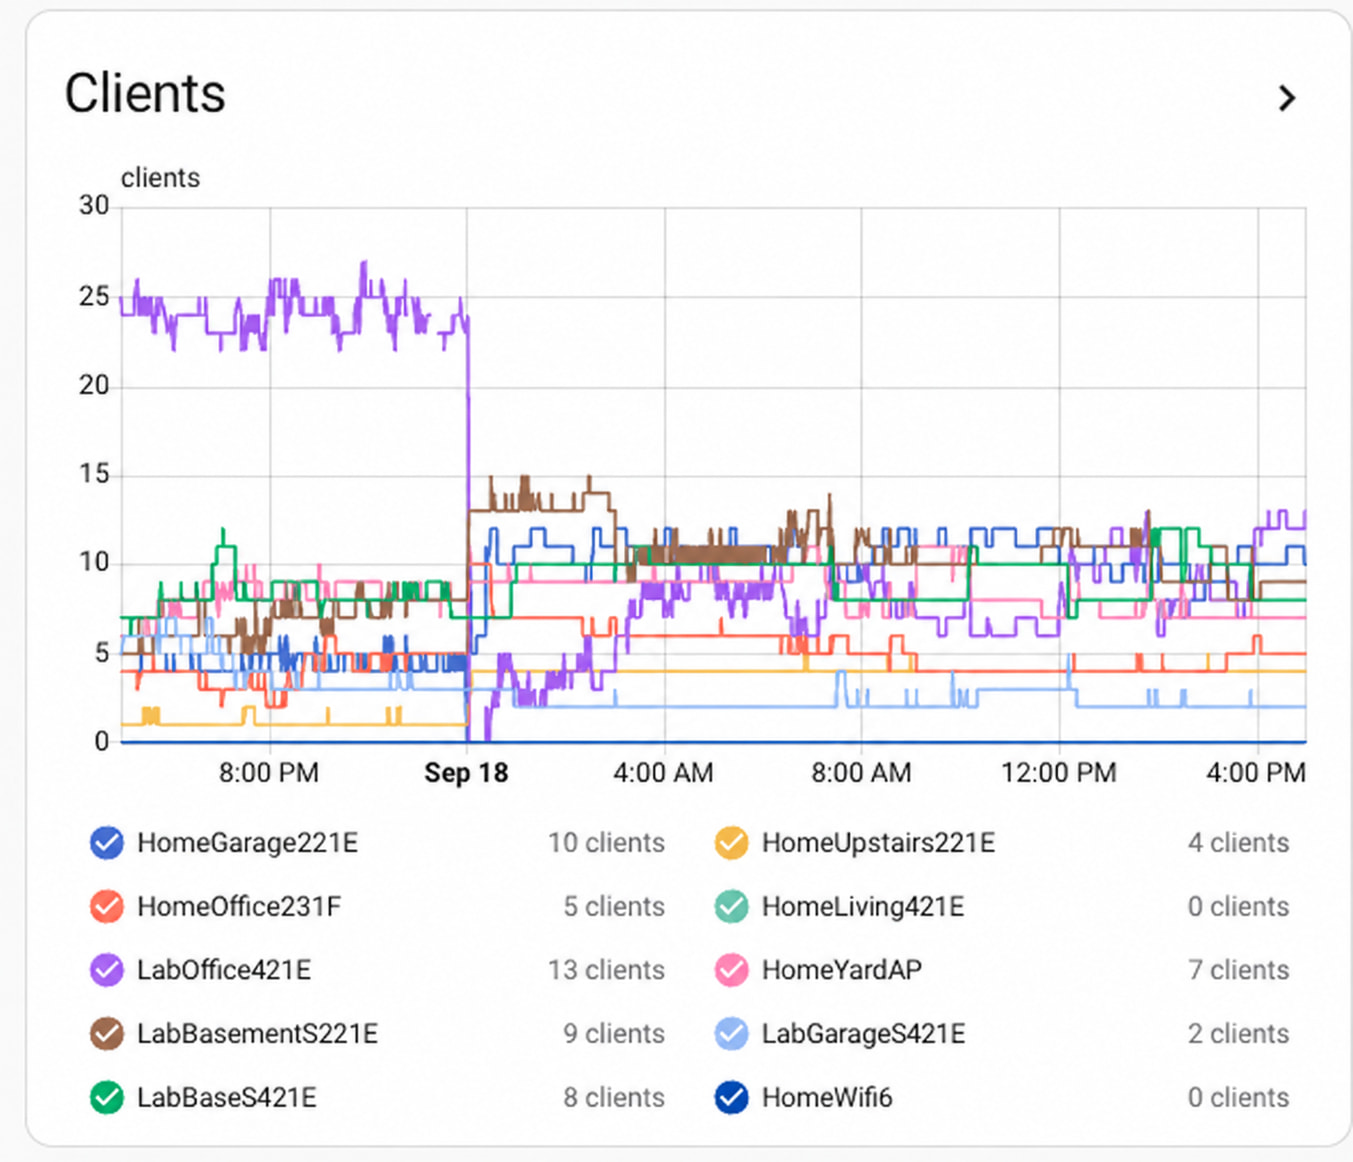
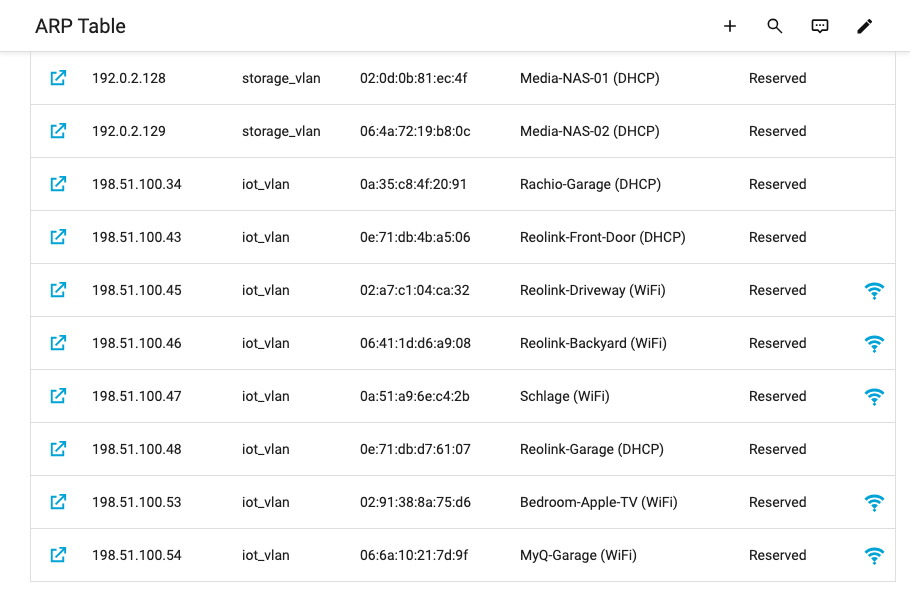
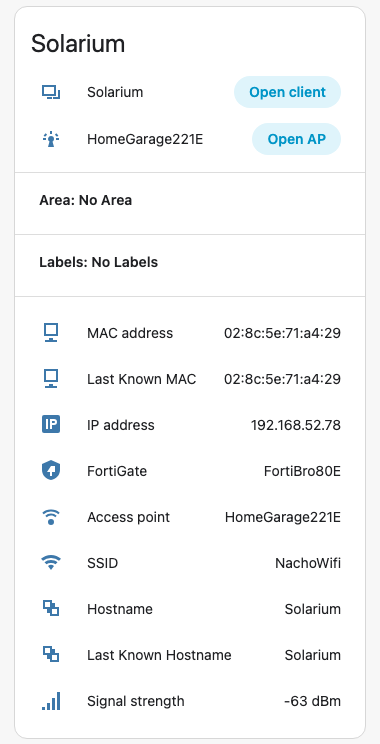
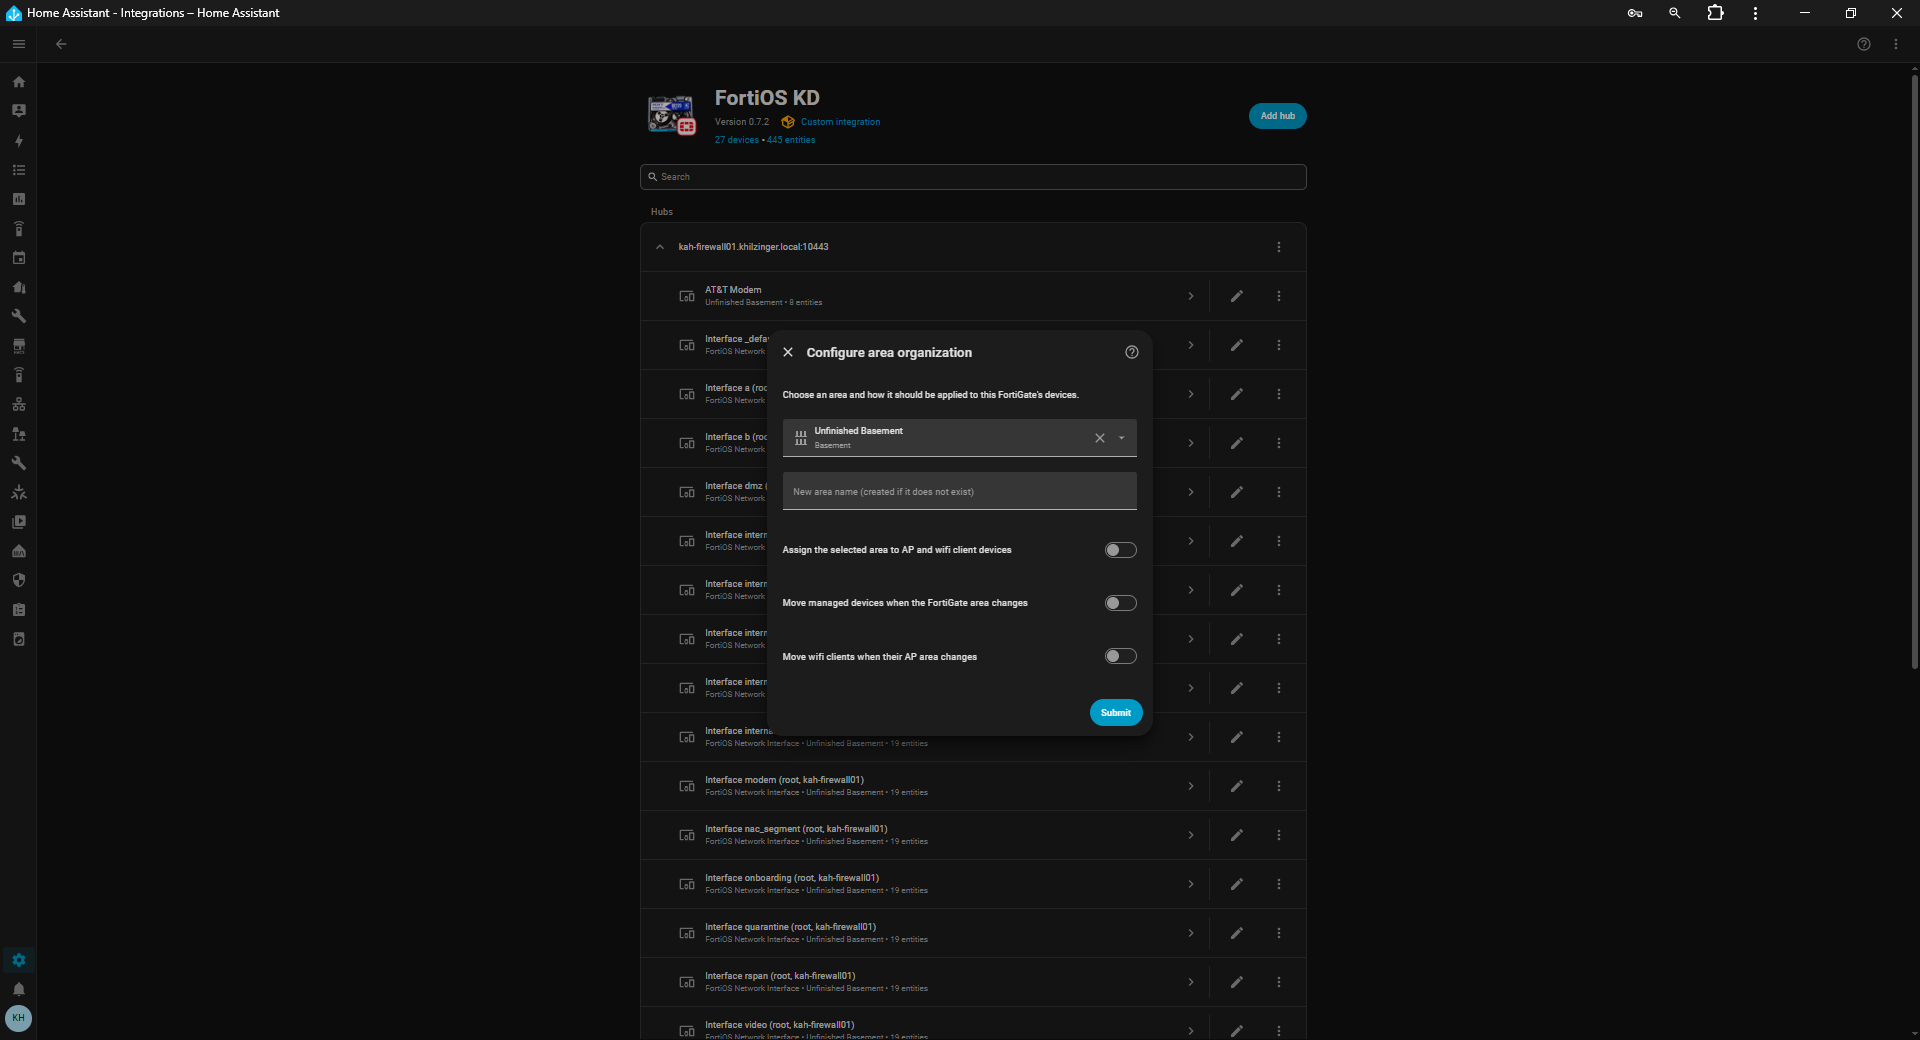
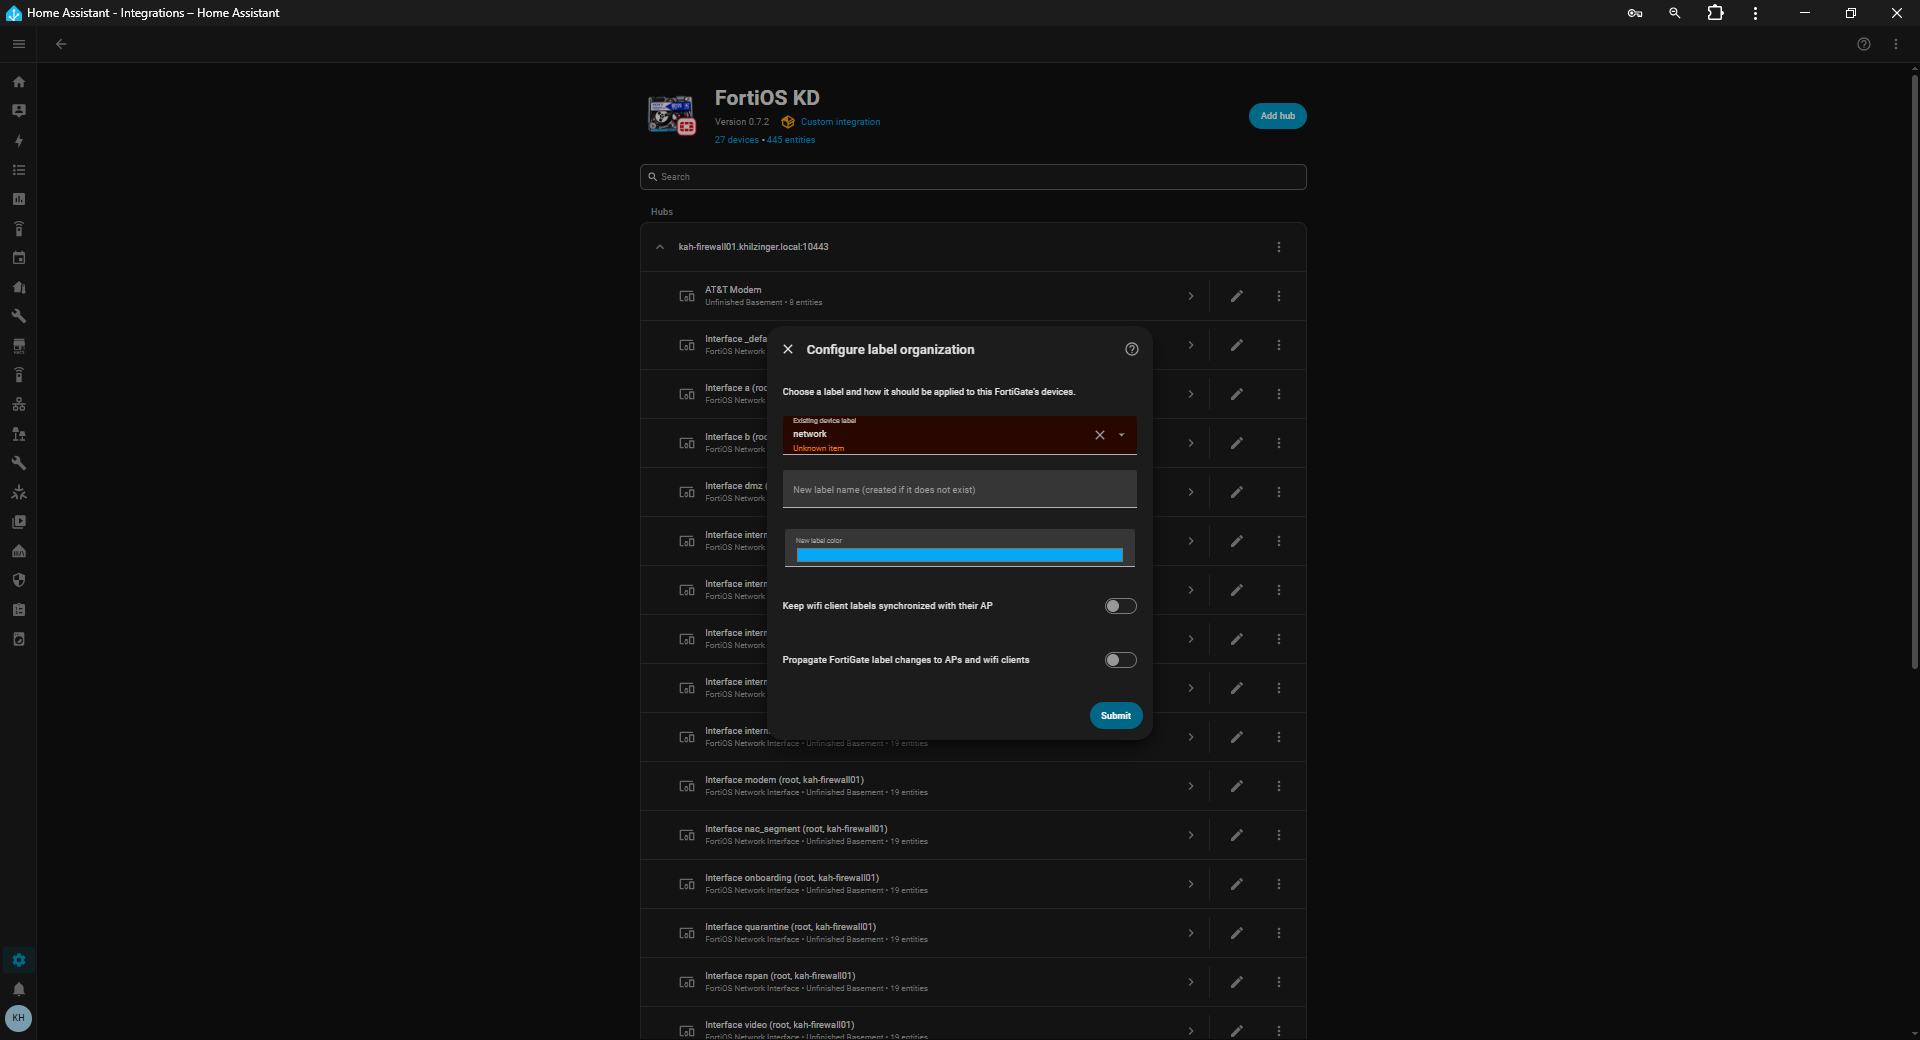
I’ve been building FortiOS KD, an unofficial Home Assistant custom integration that locally polls FortiGate firewalls using a read-only REST API account.
The integration has been tested with FortiOS versions spanning 6.0 through 7.2. FortiOS 6.2 can optionally use SNMPv2c for ARP data because that release does not provide the newer REST ARP endpoint.
Open the three-dot menu and select Custom repositories.
Add https://github.com/thekerneldump/fortios-kd as an Integration.
Install FortiOS KD, restart Home Assistant and add it from Settings → Devices & services.
The project is still under active development, and I’m looking for people interested in testing it—especially across different FortiGate models, FortiAP models and FortiOS releases.
If you try it, please let me know what works, what data is missing and whether you encounter any version-specific API differences. Issues and feedback are welcome on GitHub.
FortiOS KD is an independent community project and is not affiliated with or endorsed by Fortinet or the Home Assistant project.
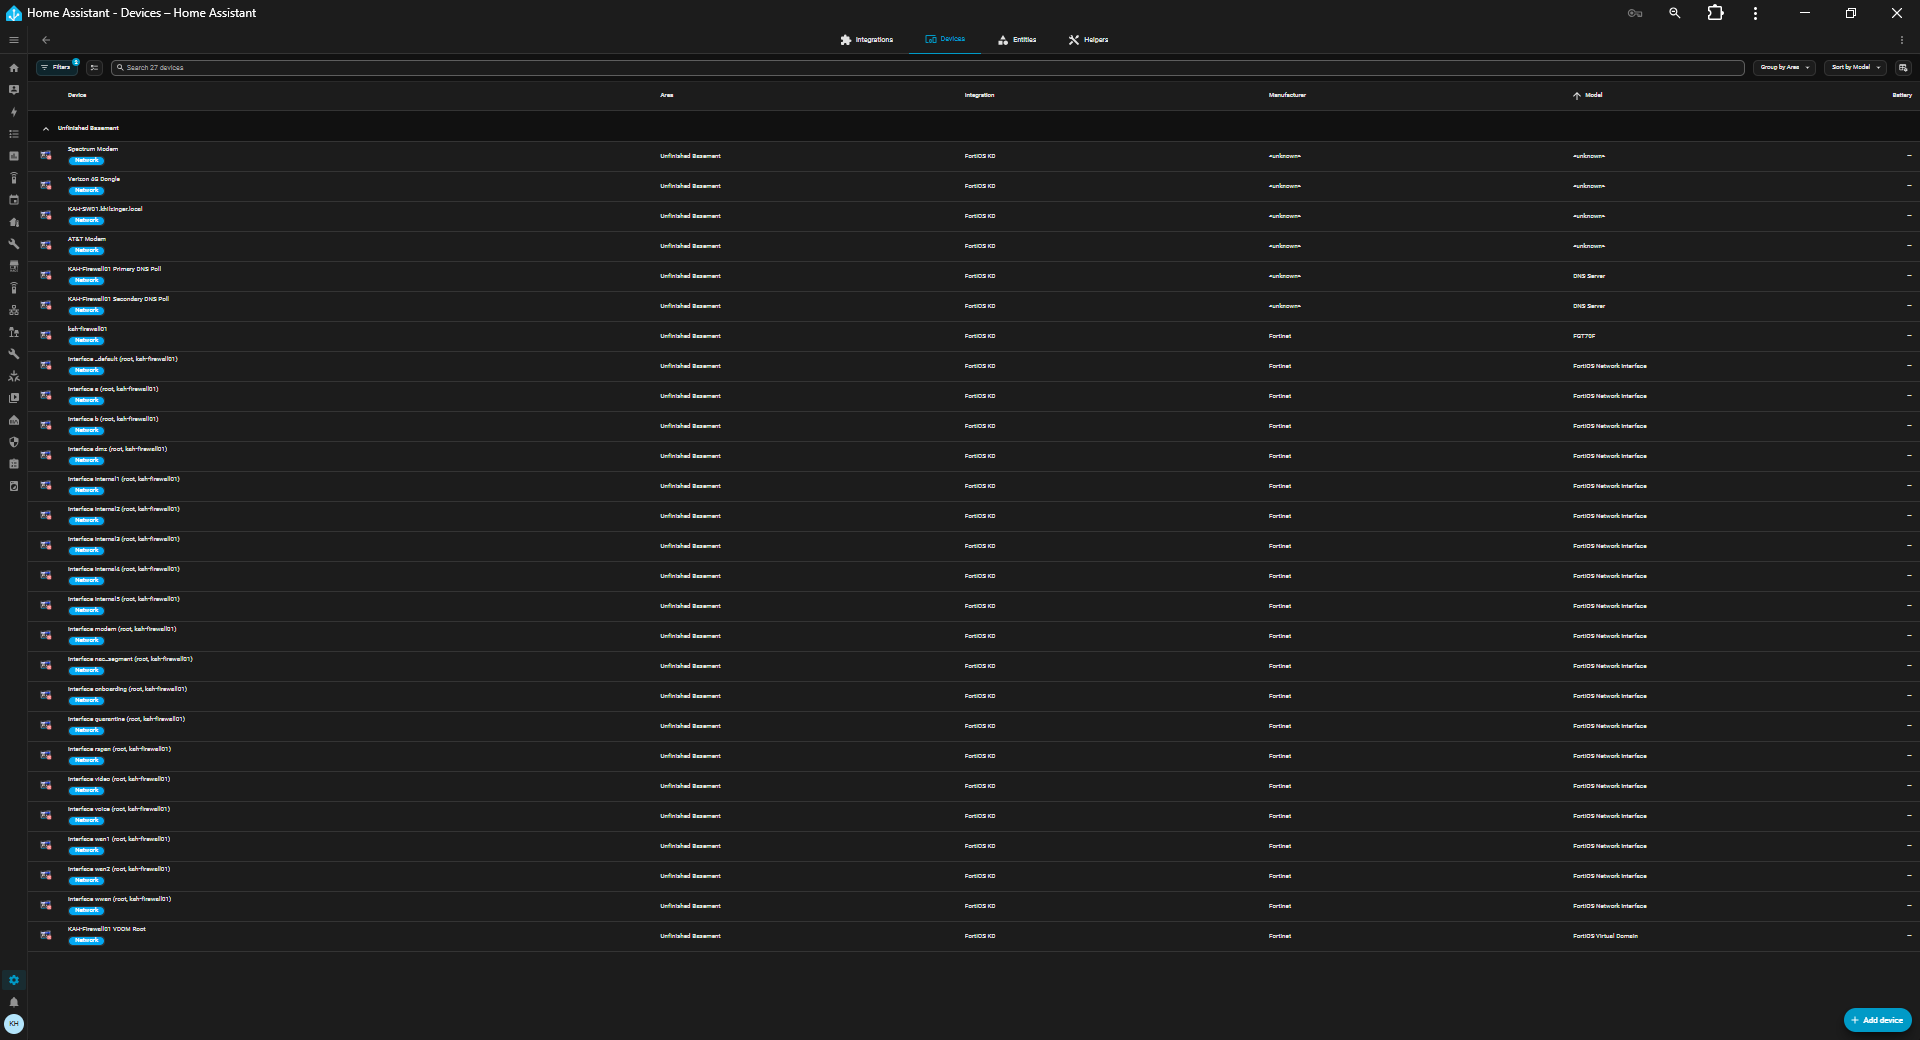
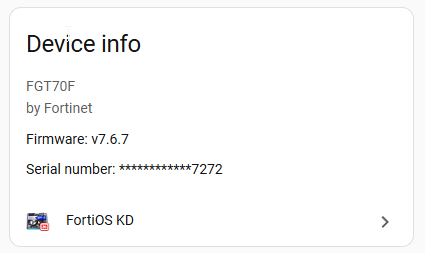
Installed it!!! I do not use FortiAPs so it is very much limited as far as the Firewall stuff. I do see serial number (no need for me to mask it from myself) and version number. I do like how it pulled the ARP information as entities and I labeled them as my switch connection, and 3 Internet connections (yes, that level of nerd where i have 2 1GB connections AND cellular backup)
I love how it uses a RO API key.
I have the FortiGate Policy Automation from HACS for the policies. That seems to work well. Now, my OCD is making me enter missing comments on my policy.
I would like to see additional things in this integration, like CPU, Memory, whether or not it is on Conserve, Sessions, Interface bandwidths, SD-WAN (I use that to choose between my Internets).
Nice to haves would be DNS resolution times, Botnet Activity, virtual IP hit counts (I have those for my two Plex servers across both gig Internets), and maybe traffic shaping.
AWESOME JOB!!! I cannot wait for all you come up with and consider me a Beta Tester.
I actually want to use HA as a network monitoring software and can do Unifi and this seems like a start for FortiNet. I do have one FortiSwitch. I WISH there was better for my main Cisco switch.
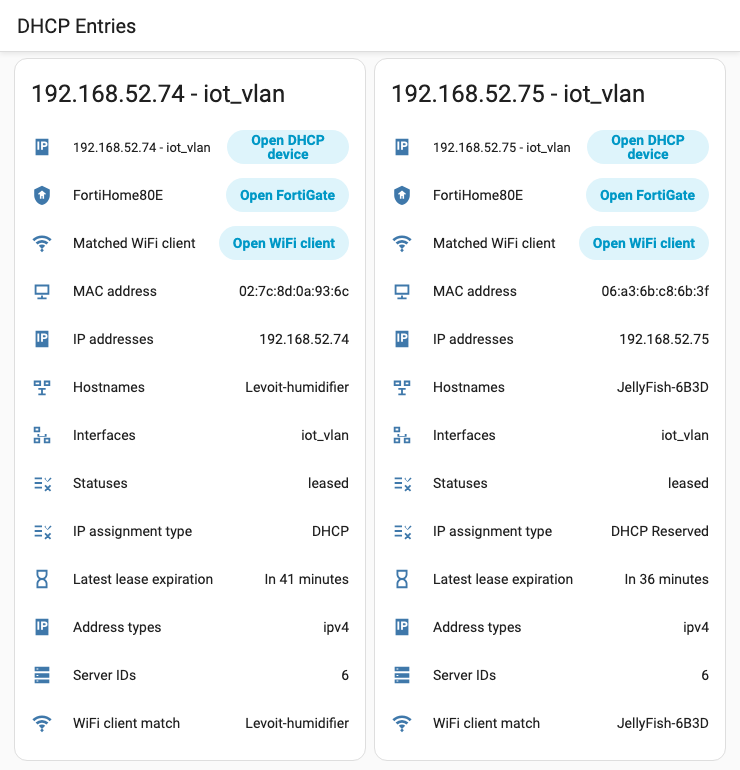
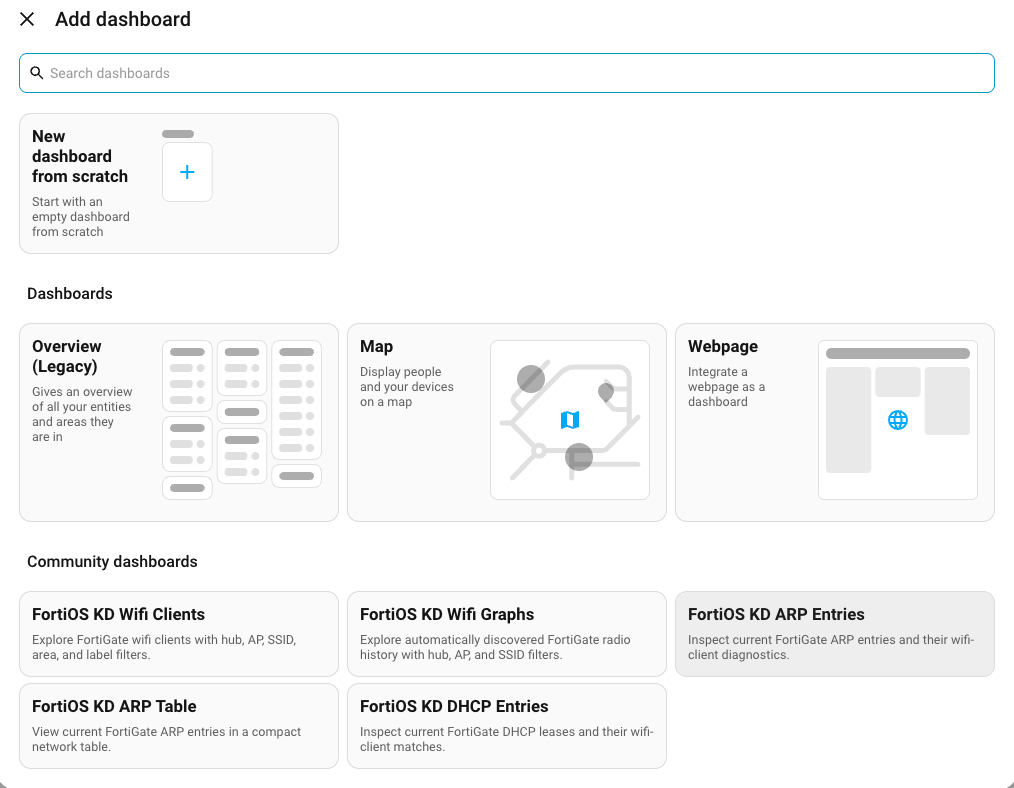
I am so glad you enjoyed it. I am going to add policies as well, it was really my initial motivation but I got side tracked into doing the wifi stuff because I just installed some new APs outside and wanted to watch myself roaming as I walked around. CPU, Memory, Policies, sessions all that I am going to add…I’m iterating on it relatively quick because I really want something I can use all the time. One thing I will do is if you label a DHCP reservation (or as soon as i add devices, a device), I want to give you the option to propagate that label down to the ARP entry and the DHCP entry so you can at-a-glance find everything about a specific link. Have you tried adding the custom dashboards? If you go to dashboards in your HA settings, then click Add dashboard, you can see the custom dashboard strategies I added.
You may need to hit ctrl-command-refresh to refresh it. But you can add them to your side bar and I have all sorts of filters in there so you can filter by firewall if you have more than one, by interface (vlan), and so on.
I also have a ton of Fortiswitches. Mostly 108E, 124E, I think a 124F, a bunch of 108E-FPO E and 108E-POE, so I’m also going to make an integration for the switches. I don’t use the fortilink on my firewall to connect my switches but I will definitely hang one off a firewall so I can add that functionality to the integration.
This release adds VDOM discovery, per-VDOM resource monitoring, and a dedicated VDOM dashboard.
What’s new
Discovers configured VDOMs and represents them as devices linked to their FortiGate.
Adds management-VDOM identification and VDOM-name diagnostics.
Adds per-VDOM sensors for:
CPU usage
Memory usage
Active sessions
Session usage percentage
Adds the KD VDOM Resources dashboard strategy.
Adds Firewall and VDOM dashboard filters.
Supports combined resource graphs for comparing VDOMs, or separate graphs for each VDOM.
I personally like to see multiple firewalls (I have like 8 of them) on a single graph so I can see the outlier… but I recognize some folks want to see individual cards for each firewall, so I added a dropdown box that lets you pick the format you want.
Added an editable Preferred name to each FortiGate. Dashboard labels, graph legends, and firewall filters use this name without renaming the Home Assistant device.
Added VDOM-scoped DNS server devices discovered from global DNS configuration and enabled per-VDOM overrides.
Added DNS server diagnostics for IP address, VDOM, configuration source, configured role, latency, and last-tested time.
Added a DNS server summary to each VDOM device.
Added configured DNS-server latency graphs to the KD VDOM Resources dashboard.
Runtime DNS latency enriches configured DNS servers but does not create devices for unconfigured addresses.
Preserved Home Assistant 2025.12-compatible device relationships.
DNS latency legends
The combined all-firewall view uses Firewall name - DNS IP so every series remains unambiguous. Long labels may be visually truncated, but the complete name is available in the graph hover details. Selecting one firewall or using Separate by VDOM provides compact IP-only labels.
FortiOS KD 0.7.2 — Device Inventory and Interface Monitoring
This release adds optional detected-device inventory, detailed interface
monitoring, and two new dashboard strategies for exploring that data.
Detected-device inventory
FortiOS KD can now import the devices identified by your FortiGate and
represent them as independent Home Assistant devices.
New information includes:
Hostname and identification source
IPv4 and IPv6 addresses
MAC and master MAC addresses
Interface and last-seen time
Operating system and software version
Hardware vendor, type, family, and version
The source FortiGate used to identify each attribute
OUI-derived vendor information
A diagnostic warning when FortiGuard’s vendor identification may be incorrect
Recently seen and stale status sensors
Inventory-change diagnostics without retaining previous sensitive values
Detected-device information can also enrich matching ARP, DHCP, and Wi-Fi
client devices. When no better hostname is available, the inventory hostname
is shown with (Device Info) to make its source clear.
KD Device Table
The new KD Device Table provides a compact inventory view with filters for:
FortiGate
Hardware vendor
Hardware type and family
Operating system and software version
Interface
Devices last seen before or after selectable time thresholds
Exact MAC matches link related Wi-Fi clients without merging the separate
device records.
Interface monitoring
Optional interface synchronization now creates devices for physical and VLAN
interfaces across every available VDOM.
Interface devices include:
Name, alias, IP address, and prefix length
Link state, speed, and duplex
VLAN ID and parent interface
TX and RX data rates
TX and RX packet rates
TX and RX error rates
Rates expressed in both megabits and megabytes per second
Each interface includes an editable Preferred name used by graph legends.
It initially follows the FortiGate interface alias, but a Home Assistant
override remains in place unless that alias changes on the FortiGate.
KD Interface Graphs
The new KD Interface Graphs dashboard includes:
Mbps graphs first, followed by MB/s, packet-rate, and error-rate graphs
Combined and separated-by-firewall layouts
FortiGate, link-state, speed/duplex, and parent-interface filters
Independent controls for hiding hardware-switch members and Wi-Fi SSID
interfaces
Time ranges from 30 minutes through one week
Preferred interface names in graph legends
Wider graph cards for improved readability
Performance and compatibility
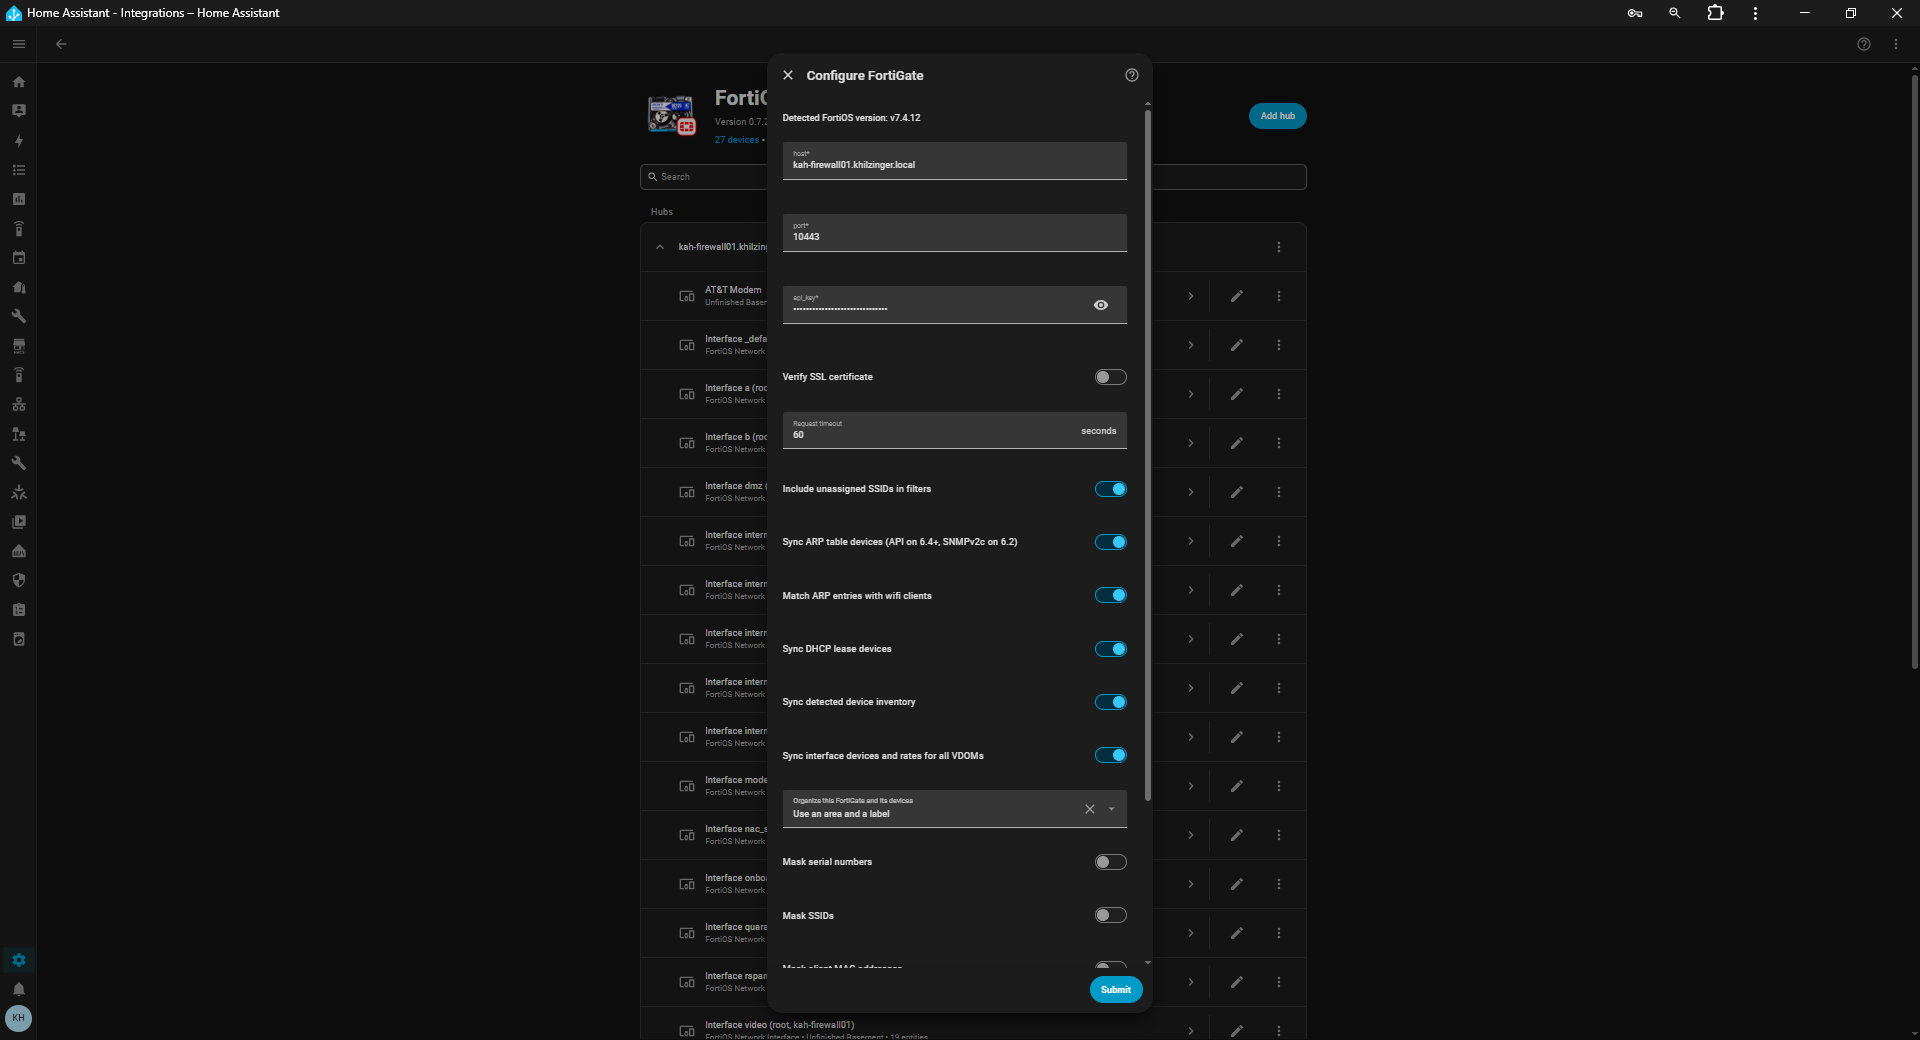
Detected-device and interface synchronization are disabled by default,
allowing each FortiGate to opt in independently.
Detected-device inventory is refreshed every five minutes.
Upgrade notes
Enable Sync detected devices or Sync interfaces from the FortiOS KD
integration settings after upgrading.
The first interface-rate sample is unavailable until a second counter reading
is collected. Rates also briefly become unavailable after a counter reset
instead of reporting an incorrect negative value.
Those entities (from what I could tell) are the filters the integration is creating for the dashboard strategies. They are technically entities but they are not entities related to your firewall devices, but rather objects that the dashboards use to filter the different items.
Sounds great! I made sure that all features are “opt in”… in case it overwhelms your HA with all the entities. I see you masked your serial number, which my thought process for adding privacy masking to everything was posts like this. I like the idea of not having to sanitize your screenshot before posting it… rather just mask everything and turn it off when you are done. Try out the dashboards… you may have to hit ctrl-command-R to refresh the “dashboards” settings screen, then click add and you’ll see them all at the bottom.