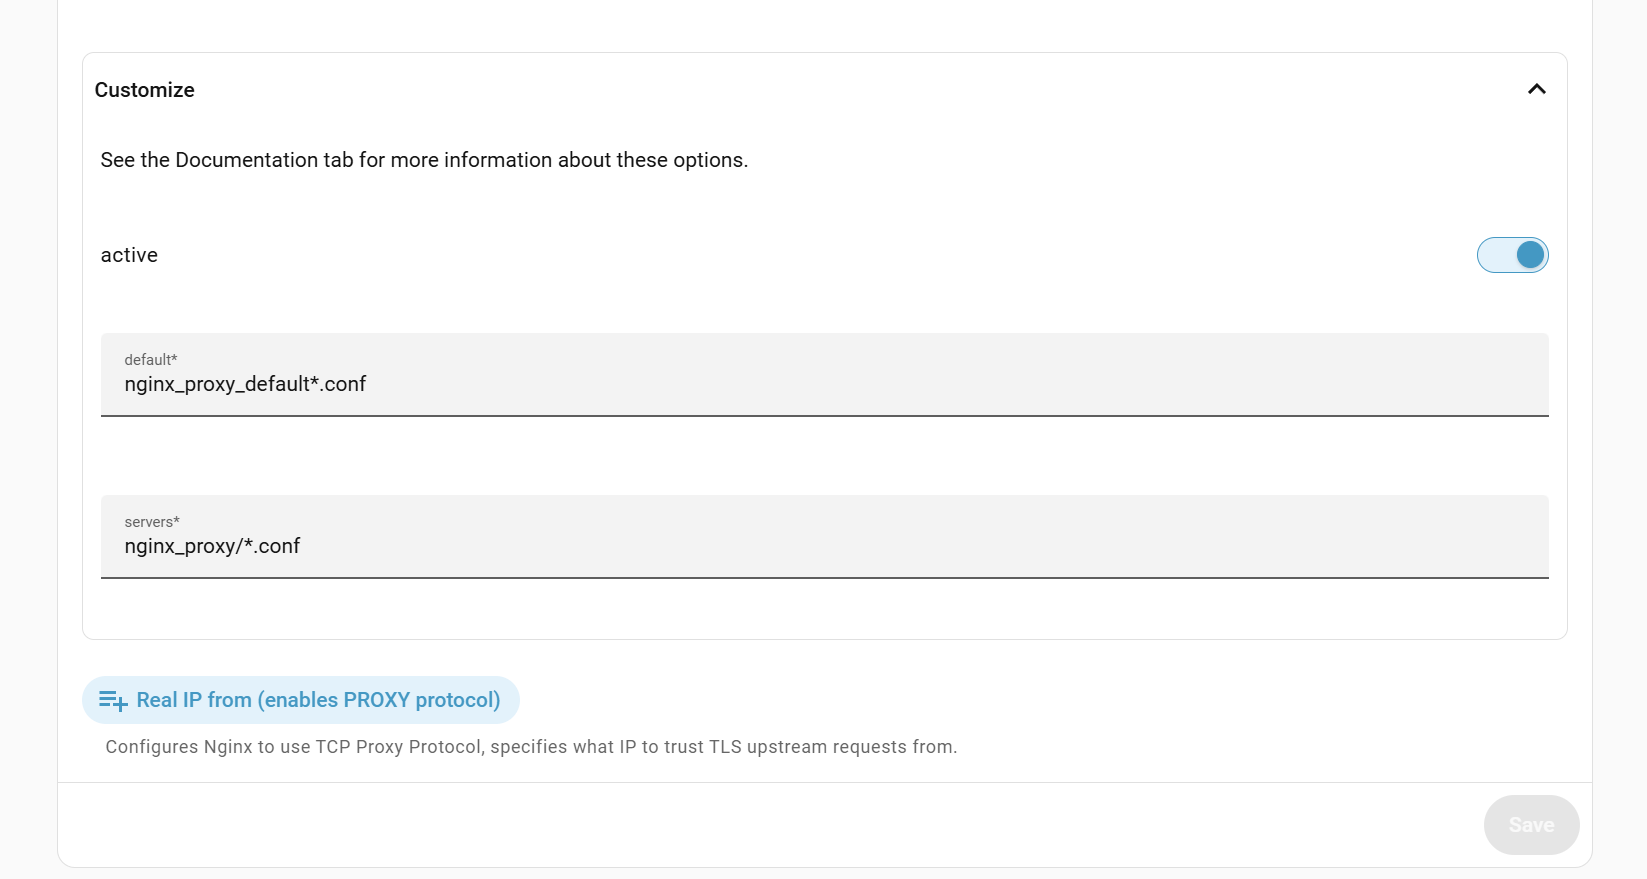
Aided by AI run tests and when running an external curl test against http://mydomain.duckdns.org it results in html and AI tells me it’s becuase “The return of the Home Assistant login screen HTML means NGINX is completely ignoring the custom file mapping.”
Not sure how to progress as AI keeps taking me in circles to fix paths none of which works.
I am trying to complete the tesla public key external test (either by using a URL in a browser or a curl test).
But any curl test for public keys (either the site’s or the tesla one) ends up either in 404 not found or sending me the home page for the site. AI tells me that NGINX is passing the request to HA which doesn’t know what to do so is throwing those replies. AI is telling me to add python script etc etc… which I’m not comfortable doing. I’ve already recreated the /.well-known folder structure under /share, /config, /config/www, /var/www - I fear I am just adding complexity to the site.
Surely it cannot be this difficult for a standard App like NGINX to just be installed and configured and work? Why is it passing stuff to HA which then shits itself? How do I fix this?
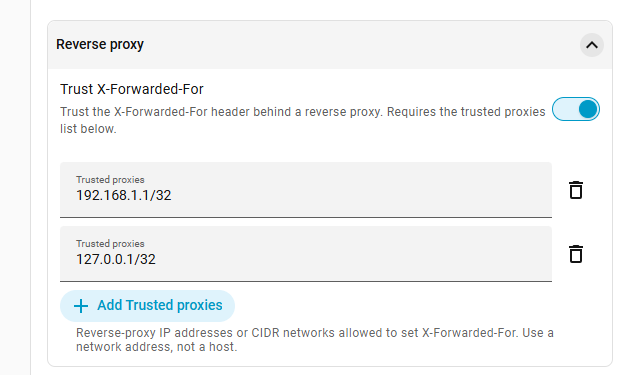
After the 2026.8 change in HA I had to add the following in under settings / network reverse proxy to get NGINX and Duckdns working correctly. The docs on NGINX have not been updated. HTML is NOT in Yaml anymore. You will notice the trusted proxy called out in the docs is not in mine. Playing around and asking I was told it is not needed with my confirguration. the 127.0.0.1 is my local loop back and the 192.168.1.1. is my router IP. It took me awhile, but once I did this I have been stable.
I am using HAOS so it may not be the same for you. I can access the network both internally and externally with no errors as I have for years prior to 2026.8. I never really studied networking and was not understanding what I was doing. I just copied the docs and or video information and hoped it worked. When it did I had no understanding of why? Router forwarding?, Duckdns? Nginx? Or Home Assistant misconfigured? I was not getting error messages in any log files, just connections dropping or not connecting at all.
Then did a URL and also a curl test externally to the tesla public key. Got the following reply - nothing in either the HA logs or the NGINX logs (does that mean it’s not even getting to NGINX or HA to process?)
curl -v https://tarshisdevineha.duckdns.org/.well-known/appspecific/com.tesla.3p.public-key.pem
*   Trying 202.153.217.186:443...
* Host tarshisdevineha.duckdns.org:443 was resolved.
* IPv6: (none)
* IPv4: 202.153.217.186
* ALPN: curl offers h2,http/1.1
* TLSv1.3 (OUT), TLS handshake, Client hello (1):
* SSL Trust Anchors:
*   CAfile: /etc/ssl/certs/ca-certificates.crt
*   CApath: /etc/ssl/certs
* TLSv1.3 (IN), TLS handshake, Server hello (2):
* TLSv1.3 (IN), TLS change cipher, Change cipher spec (1):
* TLSv1.3 (IN), TLS handshake, Encrypted Extensions (8):
* TLSv1.3 (IN), TLS handshake, Certificate (11):
* TLSv1.3 (IN), TLS handshake, CERT verify (15):
* TLSv1.3 (IN), TLS handshake, Finished (20):
* TLSv1.3 (OUT), TLS change cipher, Change cipher spec (1):
* TLSv1.3 (OUT), TLS handshake, Finished (20):
* SSL connection using TLSv1.3 / TLS_AES_256_GCM_SHA384 / X25519MLKEM768 / id-ecPublicKey
* ALPN: server did not agree on a protocol. Uses default.
* Server certificate:
*   subject: CN=tarshisdevineha.duckdns.org
*   start date: Sep  7 07:12:28 2026 GMT
*   expire date: Dec  6 07:12:27 2026 GMT
*   issuer: C=US; O=Let's Encrypt; CN=YE1
*   Certificate level 0: Public key type EC/secp384r1 (384/192 Bits/secBits), signed using ecdsa-with-SHA384
*   Certificate level 1: Public key type EC/secp384r1 (384/192 Bits/secBits), signed using ecdsa-with-SHA384
*   Certificate level 2: Public key type EC/secp384r1 (384/192 Bits/secBits), signed using ecdsa-with-SHA384
*   Certificate level 3: Public key type EC/secp384r1 (384/192 Bits/secBits), signed using ecdsa-with-SHA384
*   subjectAltName: "tarshisdevineha.duckdns.org" matches cert's "tarshisdevineha.duckdns.org"
* OpenSSL verify result: 0
* SSL certificate verified via OpenSSL.
* Established connection to tarshisdevineha.duckdns.org (202.153.217.186 port 443) from 192.168.1.75 port 49162
* using HTTP/1.x
> GET /.well-known/appspecific/com.tesla.3p.public-key.pem HTTP/1.1
> Host: tarshisdevineha.duckdns.org
> User-Agent: curl/8.21.0
> Accept: */*
>
* Request completely sent off
* TLSv1.3 (IN), TLS handshake, Newsession Ticket (4):
* TLSv1.3 (IN), TLS handshake, Newsession Ticket (4):
< HTTP/1.1 404 Not Found
< Content-Type: text/plain; charset=utf-8
< Referrer-Policy: no-referrer
< X-Content-Type-Options: nosniff
< Server:
< X-Frame-Options: SAMEORIGIN
< Content-Length: 14
< Date: Tue, 08 Sep 2026 10:32:55 GMT
<
* Connection #0 to host tarshisdevineha.duckdns.org:443 left intact
404: Not Found#
I’m no networking expert but it seems it all goes well until this GET command:
GET /.well-known/appspecific/com.tesla.3p.public-key.pem HTTP/1.1
which causes the error as it can’t find the file or path?
I have tried moving/copying the public key to a slew of different folders under the structure (including this one) to try and make it visible externally. None of them worked. I will try this one now and report back.
I have some questions of what you’re suggesting above:
under NGINX settings customize, there is nothing in the UI showing a server block so can I assume correctly you want me to check the config YAML settings?
Have you heard about Google Search ?, or Read nginx Beginner Guide ?
PS: There is also a search function in this Forum !
Some of your “specific” issues in configuring your NGINX, could be used as search-words
Beside ofcause the official docs for nginx and ssl ( + Local access ) in HA
I can’t seem to find the NGINX config file. According to the Beginner’s Guide:
A signal may also be sent to nginx processes with the help of Unix tools such as the kill utility. In this case a signal is sent directly to a process with a given process ID. The process ID of the nginx master process is written, by default, to the nginx.pid in the directory /usr/local/nginx/logs or /var/run
I have looked in all of the directories and cannot find a nginx.pid file anywhere. When I try to search for all files with nginx* wildcard:
So no idea where the nginx config file is. And I suspect this may be the issue as paths to keys are not resolving. There is clearly a /share/nginx_proxy_default_tesla.conf file with the path to the tesla key, but that doesn’t seem to be working/being picked ip.
Good, that’s because you use HTTPS
( NOTE: even i get to your HA, using the external DOMAIN.url )
What exactly is your “Issue”, can’t you log in locally ?, In that case … Change Your Topic Header !
IS It, just the “external” curl-tests, that “fails”, And what’s the reason for you obsession of trying these curl’s with http/https ?
( would you feel more “comfortable” if also a “get”-test to your internal " public-key.pem " file would work, externally ) ?
Is Your “issue” That You can’t login(get to your login-screen) Locally ?, then Change your Topic Header to reflect that !
And provide relevant info of the settings you’ve done in HA, to be able to login Locally, also with which url, you can’t access HA with , Locally
( NOTE: I assume you have followed the official documentation, for this purpose, and Not AI OR You-Tube )
PS: Just out of courtesy.
As you now 11 Days ago “Published” Your “Domain-Name” , Your’s and everyone else’s AI’s, Bot’s and Crawlers most likely have this “Listed”
Meaning “Someone” is constantly “banging” on Your “Door”
And Your Public-Key ( And HA’s “local(www)path’s” ) is definitively " Public "