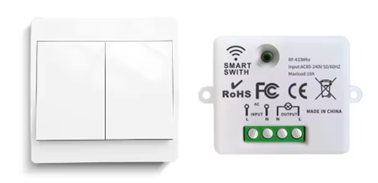
Bought a 2 gang kinetic switch from Aliexpress about 18 months ago like in the picture but without the relay. To be fair Aliexpress messaged to say the switch would only work with their hardware and I could cancel if I wanted.
OpenMqttGateway could detect it. RTL_433 app and original RTL_433.exe couldn’t pick it up.
Put my RF bridge with Tasmota in raw mode and it just got spammed by every device in the area.
Then ESPhome started supporting CC1101 and RF proxy was announced so I installed it on a old ESP32 on a perf board.
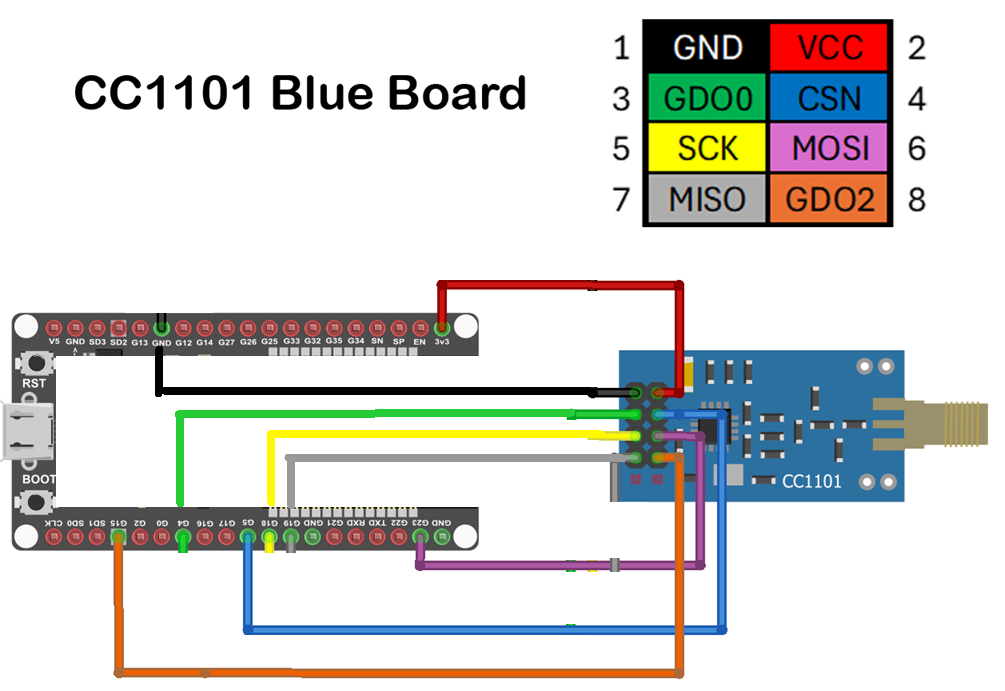
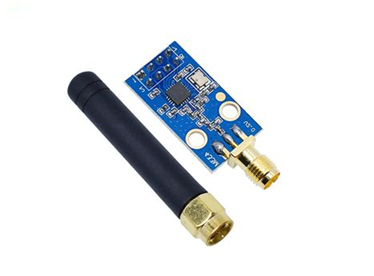
I tested the antenna that came with the CC1101 on my VNAnano. It was tuned for 2.4Ghz
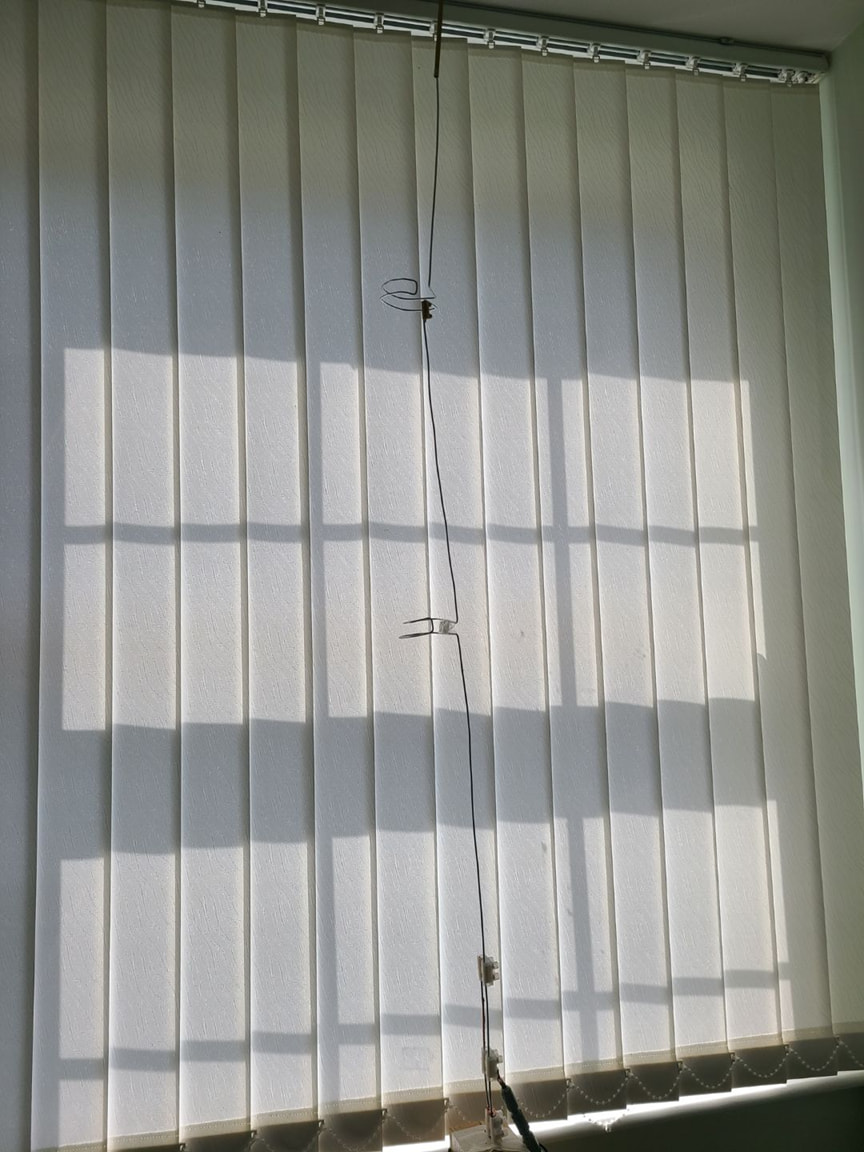
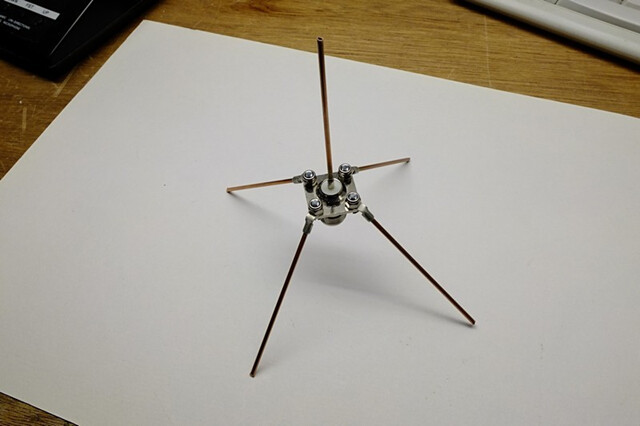
So I built my own antenna similar to the one in the pic below. I used a SMA chassie with flange. The VSWR was 1.17 when I tested it in place in the roof space of my garage.
The ESPhome could only pick it up in raw mode.
-1448, 310, -3978, 292, -3964, 311, -3973, 289, -3970, 287, -3977, 279, -4004, 237, -4033, 232 -1448, 310, -3978, 292, -3964, 311, -3973, 289, -3970, 287, -3977, 279, -4004, 237, -4033, 232
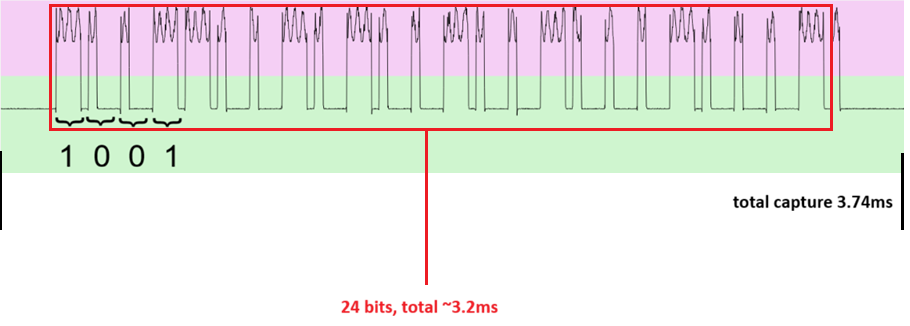
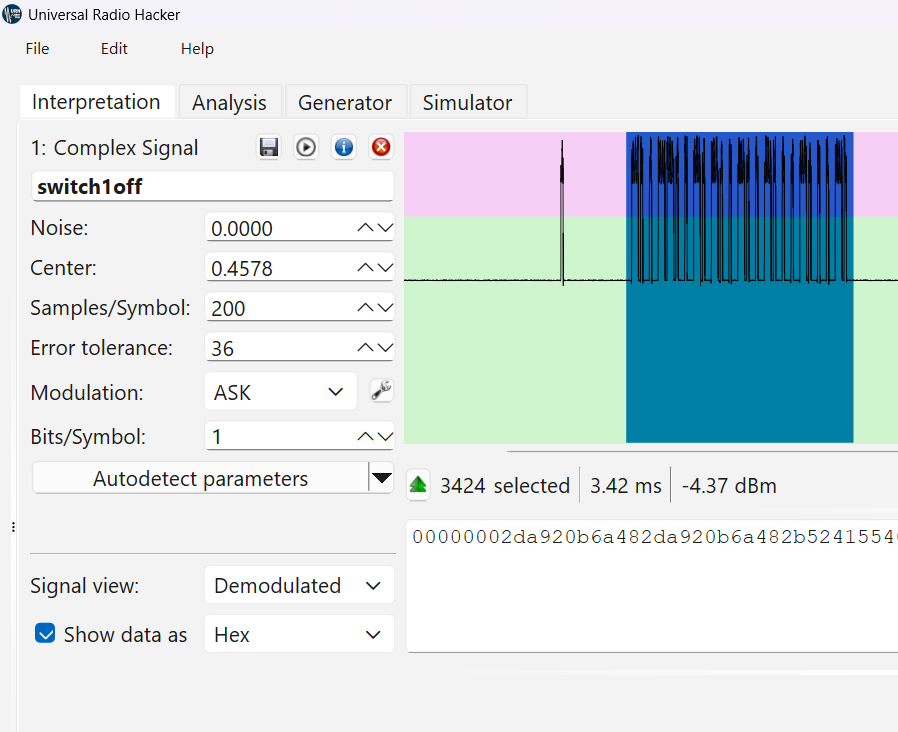
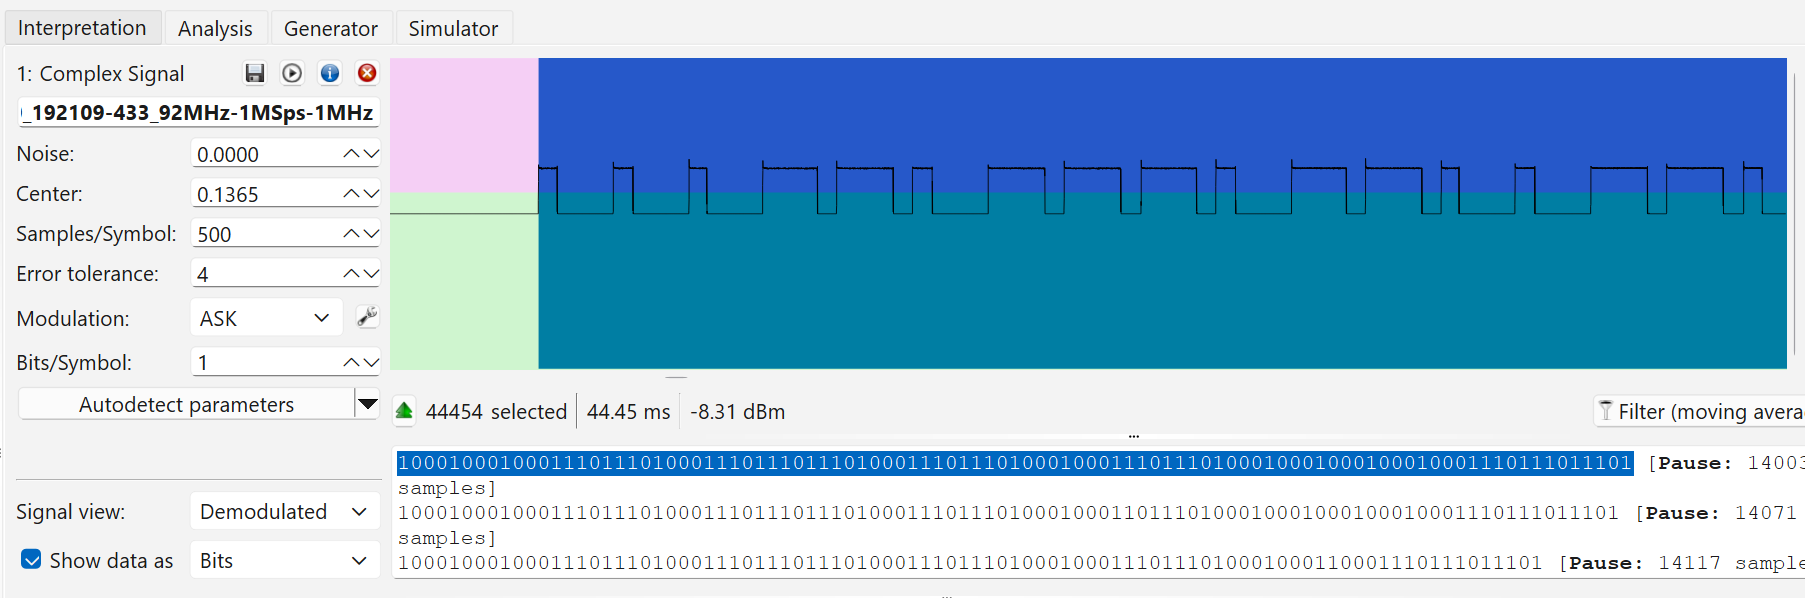
I used universal radio hacker and saw it was a repeating sequence of 7 sections each 3.74ms that were identical and 2 fading sections that weren’t the same. This is all very new territory for me but learning fast.

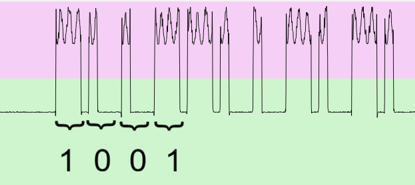
When I demodulated one of those first 7 sections I could see it was made up of 2 patterns. One was 3 highs and a low and the other was one high and 3 lows which I thought represented 1 and O. This looked the same as the coding for a door sensor that rc_switch picked up as protocol 1
That gave a code 1001100101001001000100010 on one switch but it was same code for both positions of the switch.
The other switch was 1001101100000000110100010 different from first switch but same for both positions.
It didn’t seem to work as a rc_switch binary sensor.
I then turned to use @dbuezas onlince oscilloscope to look at the raw codes.

It made the pulses look a bit more human readable. A much more simple repeating pattern.
So I just went with a binary sensor using raw. Read a lot of @Karosm posts on RF.
  - platform: remote_receiver
    name: "kinetic1"
    id: kineticone
    raw:
      code: [-1450, 315, -3970, 290, -3980, 305, -3970, 295, -3970, 280]

    filters:
      - delayed_off:
          2s
I used a shorter sequence of the raw codes. Each time you rock the switches a slightly different sequence comes out . Each number could vary by at least 30 so I went with an average.
It worked. Don’t have any plans to use it yet. It’ll have to be something low risk and very close to the ESP/CC1101
And if my wife askes. That’s how I spent saturday.
Might go back and look at those fading sections of the signal to see if anthing in there to tell the difference between rocker positions.
No AI tokens were used in the wasting of my time.