I have a Sonoff 433 MHz RF (R2 V2.2). I have flashed the RF chip with the portisch_main_OB38S003_BUCKET_SNIFFING_INCLUDED.hex following these instructions.
I have then set up ESPHome using the config below.
ESPHome config (YAML)
esphome:
  name: rf-bridge
  friendly_name: Sonoff RF bridge
  on_boot:
      then:
      - rf_bridge.send_raw:
          # think spaces must be avoided
          raw: 'AAFE55'

uart:
  tx_pin: 1
  rx_pin: 3
  baud_rate: 19200

esp8266:
  board: esp01_1m

  # Enable logging
logger:
  baud_rate: 0
# Enable Home Assistant API

api:
  encryption:
    key: !secret rf-bridge_encryption_key
  actions:  # create actions in HA
    # Send standard RF using integer values
    - action: send_rf_code
      variables:
        sync: int
        low: int
        high: int
        code: int
      then:
        - rf_bridge.send_code:
            sync: !lambda 'return sync;'
            low: !lambda 'return low;'
            high: !lambda 'return high;'
            code: !lambda 'return code;'

    # send raw RF
    - action: send_rf_code_raw
      variables:
        raw: string
      then:
        - rf_bridge.send_raw:
            raw: !lambda 'return raw;'

    - action: learn
      then:
        - rf_bridge.learn

rf_bridge:
  on_code_received:  # all firmwares, can be reported as integer, hex, or both, as desired.
    then:
      - homeassistant.event:
          event: esphome.rf_code_received
          data:
            sync: !lambda 'char buf[5]; return format_hex_to(buf, data.sync);'
            low: !lambda 'char buf[5]; return format_hex_to(buf, data.low);'
            high: !lambda 'char buf[5]; return format_hex_to(buf, data.high);'
            code: !lambda 'char buf[9]; return format_hex_to(buf, data.code);'

      - homeassistant.event:
          event: esphome.rf_code_received
          data:
            sync: !lambda 'return data.sync;'
            low: !lambda 'return data.low;'
            high: !lambda 'return data.high;'
            code: !lambda 'return data.code;'

  # Portisch only, does not do anything on RCswitch firmware
  on_advanced_code_received:
    then:
      - homeassistant.event:
          event: esphome.rf_advanced_code_received
          data:
            length: !lambda 'return format_hex(data.length);'
            protocol: !lambda 'return format_hex(data.protocol);'
            code: !lambda 'return data.code;'
ota:
  - encryption:
    platform: esphome

wifi:
  ssid: !secret wifi_ssid
  password: !secret wifi_password
  # Enable fallback hotspot (captive portal) in case wifi connection fails
  ap:
    ssid: "Rf-Bridge Fallback Hotspot"
    password: !secret fallback_hotspot

captive_portal:

# Sensors for ESP version and WIFI information
text_sensor:
  # ESPHome version
  - platform: version
    hide_timestamp: true
    name: "ESPHome Version"
  # IP address and connected SSID
  - platform: wifi_info
    ip_address:
      name: "IP Address"
      icon: mdi:wifi
    ssid:
      name: "Connected SSID"
      icon: mdi:wifi-strength-2

sensor:
  # WiFi signal
  - platform: wifi_signal
    name: "WiFi Signal"
    update_interval: 120s
  - platform: uptime
    name: Sonoff RF Bridge Uptime

binary_sensor:
  - platform: status
    name: Sonoff RF Bridge Status

light:
  - platform: status_led
    name: "Status LED"
    pin:
      number: GPIO13
      inverted: true
    restore_mode: ALWAYS_ON

button:
  # restart the ESP8285 wifi chip
  - platform: restart
    name: "Restart"

  # sending ACK can be useful for resetting uart state machine on microcontroller
  - platform: template
    name: Acknowledge
    id: ack_mcu
    on_press:
      then:
        rf_bridge.send_raw:
          raw: 'AAA055'

  # places portisch flashed microcontroller into various modes
  # commands are defined here: https://github.com/Portisch/RF-Bridge-EFM8BB1/wiki
  - platform: template
    name: Advanced sniffing start
    id: AS_start
    on_press:
      then:
        - rf_bridge.start_advanced_sniffing

  - platform: template
    name: Advanced sniffing stop
    id: AS_stop
    on_press:
      then:
        - rf_bridge.stop_advanced_sniffing

  - platform: template
    name: Bucket sniffing start
    id: BS_start
    on_press:
      then:
        - rf_bridge.start_bucket_sniffing

  # beep for 100 milliseconds
  - platform: template
    name: Beep
    id: Beep
    on_press:
      then:
        - rf_bridge.beep:
            duration: 100

  # reset microcontroller feature was added to RF-Bridge-OB38S003 custom firmware
  - platform: template
    name: "Restart radio"
    id: mcu_reset
    on_press:
      then:
      - rf_bridge.send_raw:
          raw: 'AAFE55'

  # learning mode
  - platform: template
    name: "Learning mode"
    id: learning
    on_press:
      then:
      - rf_bridge.learn
My challenge now is how to make this setup learn the RF codes from my remotes.
When I “press” the “Learning mode” button and listen for the event esphome.rf_code_received, I get nothing when I press the buttons on my remotes. The red status light on the Sonoff does nothing.
When I use the “Advanced sniffing start” button and listen for the event esphome.rf_advanced_code_received, I also get nothing. The red status light on the Sonoff turns red when I start the advanced sniffing but no events are detected.
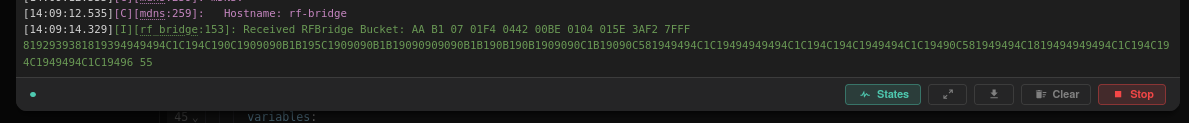
However, when I press “Bucket sniffing start” and press a button on my remote, the red status light will blink as I press the different buttons on the remote. However, the two events listed above returns nothing.
Clearly I am missing something here, can anyone point me in the right direction? How can I capture what the Sonoff bridge seemingly picks up when I use the bucket sniffing mode?